Skip to content

Tech News

Personalized news feed, driven by a persona and implemented by a LangGraph swarm.

Google froze its open source bug bounty program due to a ‘significant rise’ in AI submissions
AI/ML / techcrunch.com

Google froze its open source bug bounty program due to a ‘significant rise’ in AI submissions

Google paused its Open Source Software Vulnerability Rewards Program on October 1, citing a surge in AI-generated submissions that are mostly invalid or hallucinated. The company acknowledged that automated reports overwhelmed maintainers, echoing warnings from cybersecurity experts last year. An update is promised by Q1 2027, with participants redirected to other bounty programs.

Why it matters

For platform engineers relying on open source, this signals that AI-generated noise is becoming a significant operational burden on security programs, requiring new validation strategies.

Agents have made CI the bottleneck. Faster pipelines are the wrong fix.
AI/ML / thenewstack.io

Agents have made CI the bottleneck. Faster pipelines are the wrong fix.

Three posts landed in September that I think engineering leaders should read together. Anthropic’s engineering team wrote that their continuous The post Agents have made CI the bottleneck. Faster pipelines are the wrong fix. appeared first on The New Stack .
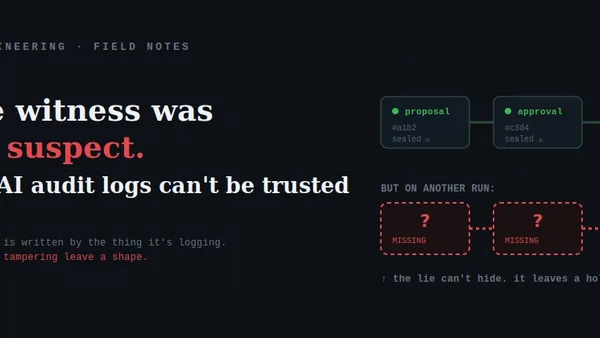
The Witness Was the Suspect: Why AI Audit Logs Can't Be Trusted
AI/ML / dev.to

The Witness Was the Suspect: Why AI Audit Logs Can't Be Trusted

An AI agent does something it shouldn't. It leaks data, or wipes the wrong database, or makes a call...

Cloudflare Fixes Cross-Tenant Data Exposure in Containers
Security / infoq.com

Cloudflare Fixes Cross-Tenant Data Exposure in Containers

Cloudflare has disclosed a cross-tenant data exposure vulnerability in Containers and Sandboxes, caused by thin-provisioned storage pools configured to skip zeroing reused blocks. Researchers recovered directory structures, database pages and complete SQLite databases across four continents. Cloudflare remediated it and found no evidence of exploitation. By Steef-Jan Wiggers

Self-hosted HTTP tunnels with SSH and Nginx
General / vincent.bernat.ch

Self-hosted HTTP tunnels with SSH and Nginx

A friend wants to proofread your work-in-progress blog post, but its preview only runs on localhost:8080 . Several tools can help. Some run as a commercial service, like ngrok or Cloudflare Quick Tunnels . Some are self-hostable but require a specific client, like frp or localtunnel . Some only require a plain SSH client but rely on a specific SSH server, like sish . Let’s implement a self-hosted solution with only OpenSSH and nginx ! $ ssh -R 0 :localhost:8080 http-over-ssh Allocated port 41535 for remote forward to localhost:8080

Aspire 13.6 Adds Persistent Dashboard Telemetry and First-Party Java and Rust Hosting
Languages / infoq.com

Aspire 13.6 Adds Persistent Dashboard Telemetry and First-Party Java and Rust Hosting

Microsoft has released Aspire 13.6. The dashboard now stores telemetry in SQLite and keeps up to ten completed runs per application. The release adds prerelease hosting packages for Java and Rust, portable volume paths, and new CLI options. Breaking changes include automatic TLS for local MongoDB resources and a new default Cosmos DB emulator image. By Almir Vuk

Using docker-compose with Podman rootless
Cloud / elou.world

Using docker-compose with Podman rootless

Using docker-compose with Podman rootless 2026-10-05 09:22:33 UTC Podman is a daemonless Docker alternative for Linux that can run without root access. However, it is less well known that Podman can expose a UNIX-domain socket compatible with the Docker API. This makes it work with most tools in the Docker ecosystem, such as docker-compose. Podman uses a Linux feature called user namespaces. With this, the root user inside a container is mapped to your host user. Other UIDs and GIDs are mapped to the ranges defined in

From: anyone@icloud.com - Spoofing Arbitrary Apple iCloud Identities
Cloud / sec-consult.com

From: anyone@icloud.com - Spoofing Arbitrary Apple iCloud Identities

From: anyone@icloud.com - Spoofing Arbitrary Apple iCloud Identities 01.10.2026 research vulnerability A case study on discovering two email spoofing vulnerabilities in Apple iCloud. (Image illustration, partially AI-generated) In the course of a research project in collaboration with the SEC Consult Vulnerability Lab, Timo Longin ( @timolongin ) - known for SMTP smuggling - discovered two exotic email spoofing vulnerabilities in Apple iCloud's emailing infrastructure. At the end of 2023 SMTP smuggling made a dramatic entrance, allowing email spoofing for millions of email servers worldwide.…

Hacking the Go compiler to efficiently map IPv4 to IPv6
General / vincent.bernat.ch

Hacking the Go compiler to efficiently map IPv4 to IPv6

netip.Addr features an Unmap() method returning the unwrapped IPv4 contained in an IPv4-mapped IPv6 address : from ::ffff:203.0.113.10 or ::ffff:cb00:710a , it returns 203.0.113.10 . 1 There is no Map() or To6() method for the reverse direction. Such a method is trivial to implement, but Go maintainers have rejected it on the grounds that users should write netip.AddrFrom16(ip.As16()) and let the compiler optimize it. 2 Today, this pattern is eight times slower than a native method. How can we teach the compiler to optimize this sequence?

My Health Check Watched the Wrong File
AI/ML / dev.to

My Health Check Watched the Wrong File

I wrote a rule for my own agents: Liveness is not usefulness. Artifact age beats PID. A job that is...