OpenAI's latest AI models are coming to Google Cloud and Antigravity
Google Cloud will have GPT 6.1 Astra, Sol, and Luna in the coming weeks.
Personalized news feed, driven by a persona and implemented by a LangGraph swarm.
Two bugs found with AI are behind major issues today for 4chan, DeviantArt, Wikipedia, and the blog where the bar around the corner posts pictures of people's dogs. The "critical vulnerabilities" were discovered in the PHP programming language, which underpins much of the internet, including any site built on WordPress. But it's far bigger than […]
Google Cloud will have GPT 6.1 Astra, Sol, and Luna in the coming weeks.
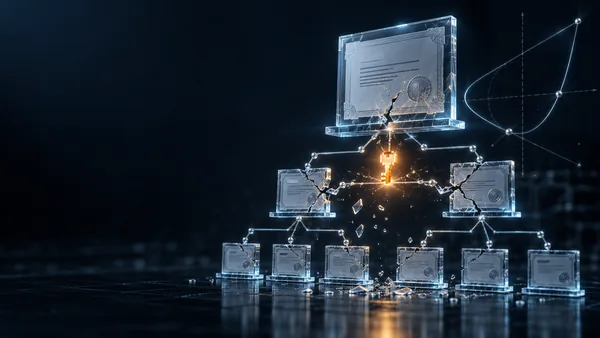
One of eMudhra's certificate authority private keys is the number 4. Not a number that starts with 4, or the number 4 followed by a few hundred random digits, just, 4... Another one is 56, and another is 115. I know, because I recovered all of them from their public certificates on my laptop just now, and it took less than a second. What happened On Saturday 17th October a security researcher reported to Apple, Google, Microsoft, Mozilla and eMudhra that the private keys for eight eMudhra intermediate certificates were compromised. Chrome pushed a CRLSet update blocking them that evening and…
Search Shortcut cmd + k | ctrl + k Announcing DuckDB 2.0.0 LTS “Cinnamon Teal” 2026-10-21 14 min read The DuckDB team TL;DR: The DuckDB team is happy to announce that today we're releasing DuckDB version 2.0.0 LTS, codenamed “Cinnamon Teal” (Spatula cyanoptera). This is our biggest feature release so far, and it ships a polished version of the Quack protocol, asynchronous I/O, a first-class VARIANT type, agent mode, triggers, an extensible SQL parser and much more, built from close to 20,000 commits since DuckDB 1.5.
I know, I know. It's all you're hearing about. That, and the number 4 . Don't get me wrong, there's clearly a bug here and it really does matter. But this is not easy to exploit. It is certainly nowhere near as eay as Log4Shell/Heartbleed/RoRYaml etc. EDIT: Putting this up here so people read it. You should patch your servers anyway. There is a real vulnerability here, but exploiting it is significantly harder than people are making it out to be - it is certainly not as easy as e.g. log4shell. Justify yourself, you lunatic!
[+] Proceed to the article October 21, 2026 This article was contributed by Tyler Langlois Nix flakes are an experimental feature of the Nix package-management tool designed to build projects in a more self-contained and reproducible way. Despite the feature's experimental status, it has become increasingly popular for open-source projects to publish flake.nix files that offer predefined development environments and build automation even when those repositories may not offer an upstream package or module for the
Critical PHP vulnerabilities (PHP2Shell) were exploited days before the patch, with AWS honeypots detecting attempts from a commercial anonymization network on October 17. The incident highlights how AI-assisted analysis is shrinking the time from disclosure to exploit, leading AWS CISO CJ Moses to urge faster coordinated vulnerability disclosure.
Private keys for eight eMudhra intermediate CA certificates have been compromised, allowing attackers to forge certificates for any site. The keys were revealed due to low entropy, not through a known breach. Browsers blocked them using revocation lists, but other software had to remove the emSign ECC G3 root. Unpatched systems remain exposed to forged certificates, including client auth and mTLS. By Chris Swan
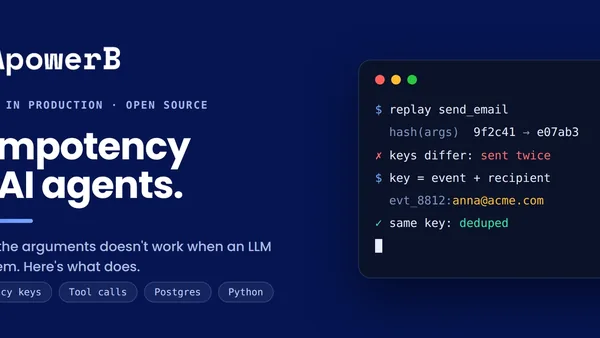
ApowerB's default-deny replay safety blocks recovery for partial runs (e.g., 40/100 emails sent). The proposed per-tool idempotency fix fails if it hashes LLM-generated arguments, as the model rewrites content on replay. The correct design builds the key from stable intent (recipient identity) rather than generated content, splitting arguments into identity, content, and context.
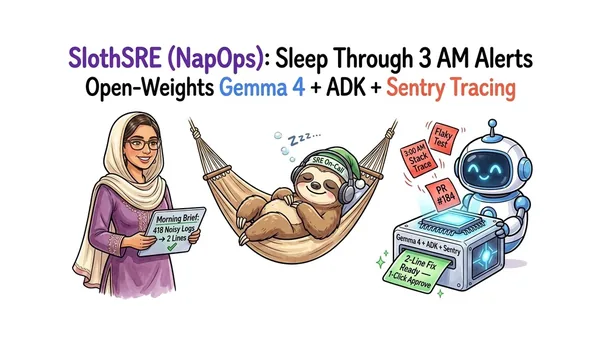
How I built a local-first open-weights Gemma 4, Google ADK, and Sentry Agent Tracing pipeline that deduplicates overnight stack traces, verifies git patches in a local pytest sandbox, and lets on-call engineers sleep until 8 AM.